Connect one security action to a business dependency you cannot afford to lose.
Choose the dependency before the tool
Start with a short list of the work you could least afford to lose: an important project folder, the email account used with clients, or the device that lets you deliver a service. That is a practical way to approach NIST’s newly released solo-business cybersecurity guide. It is an editorial reading routine, not a sequence prescribed by the agency.
NIST’s November 2 guide announcement introduces Small Business Cybersecurity: Non-Employer Firms, published as Cybersecurity White Paper 50. The NIST publication record independently carries November 2 publication metadata. The resource is intended for a business whose only paid employee is its owner, assumes no previous cybersecurity knowledge and draws selected actions from Cybersecurity Framework 2.0.
Its useful starting point is prioritisation. An owner who has identified a dependency can ask which action addresses it, what effort the action requires and how to check the result. A product catalogue starts with things to buy. This approach starts with work the business needs to protect.
Make a backup mean recoverable work
NIST’s release identifies regular backups among the guide’s practical first steps. For an owner, the important distinction is between a process that says it ran and work that can actually be recovered. Our recommendation is to try recovering an important file and opening it, rather than treating an activity notification as sufficient evidence.
Consider a hypothetical freelance designer whose unfinished projects are stored on one laptop. The question is not simply whether backup software is installed. It is whether the projects needed to continue work would remain accessible if that laptop became unavailable. The example describes a planning question, not a business observed by Foundra or a recovery test we performed.
Use the result to decide what needs attention next. If a file cannot be found, cannot be opened or is older than expected, the routine has exposed a concrete problem to investigate. A successful check is useful too, but it should not become a claim that all data is protected under every possible interruption. The check establishes only what was actually recovered.
An original way to approach the new resource
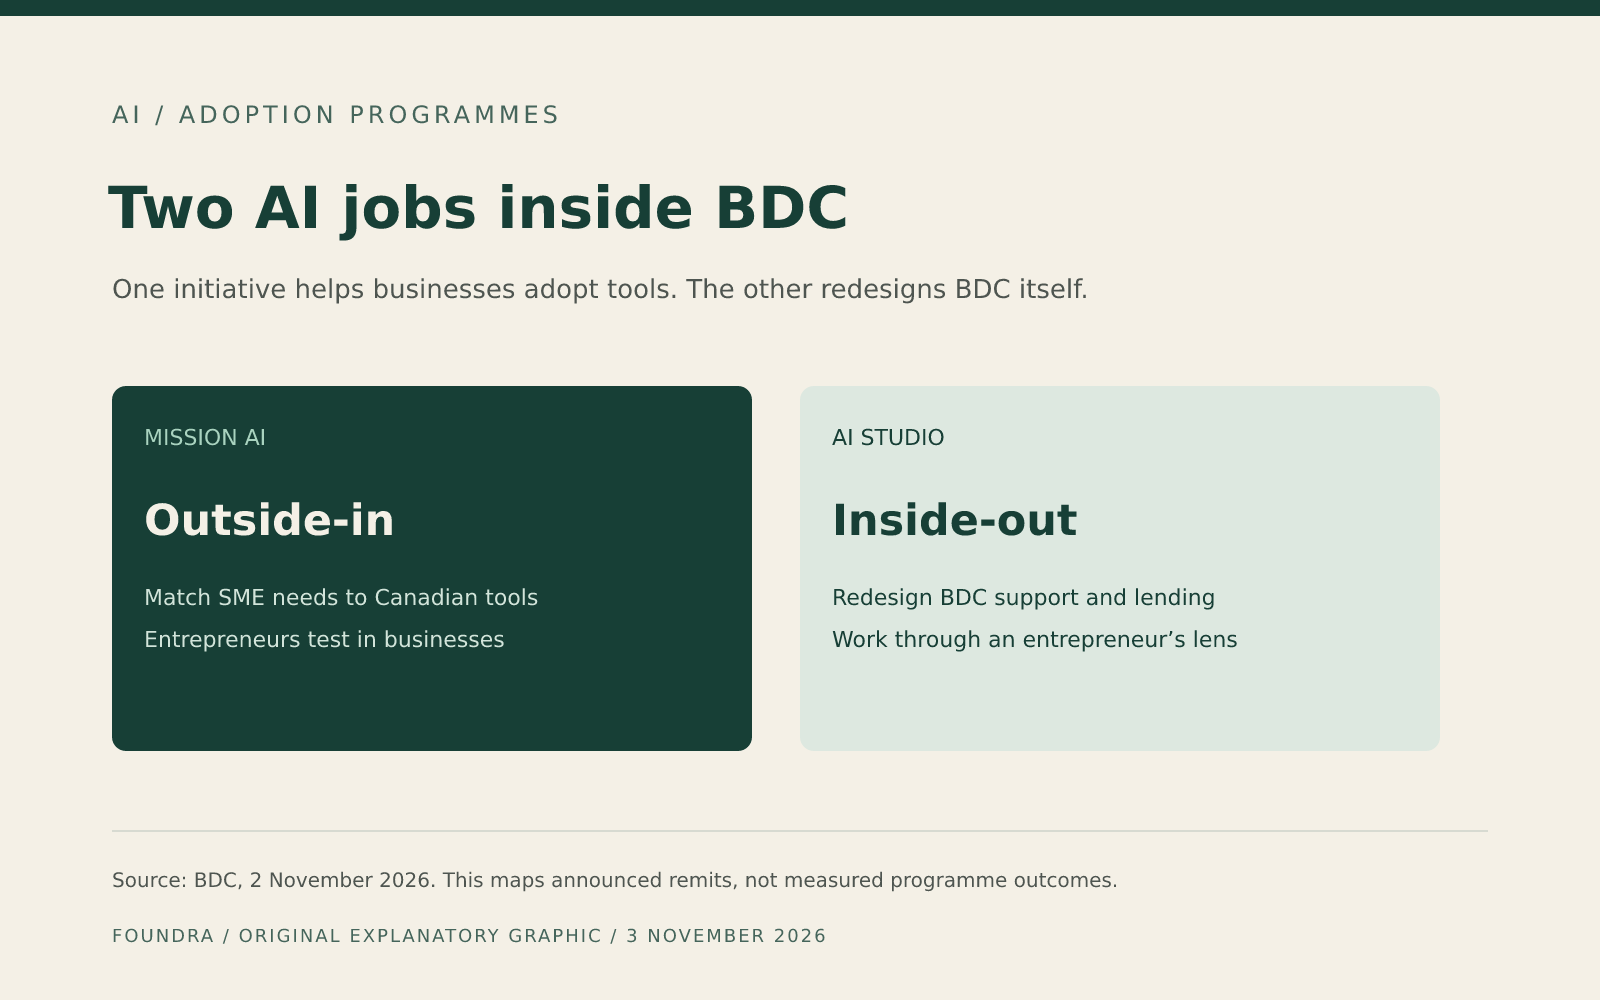
Name the dependency
Identify work or an account whose loss would interrupt the business.
Choose an action
Use the guide to select an action addressing that specific risk.
Check the result
For a backup, try recovering an important file. This is Foundra’s suggested routine, not a prescribed NIST sequence.
Fit the action to a busy week
The agency also identifies keeping software updated and changing manufacturer-assigned default passwords among actions discussed in the guide. Those examples connect security to ordinary maintenance of devices and accounts. They are not an exhaustive list of everything a particular business may need.
For the owner, repeatability matters. A manageable recurring check is easier to incorporate into work than an elaborate procedure that is rarely used and easily forgotten. Ask who can perform the action, what would signal a problem and where the relevant instructions are kept. This makes the action operational without turning it into a promise of immunity from attack.
The publication’s structure supports that staged approach. NIST says actions come with a rationale, a way to get started and options for later as the business grows. References map them to the framework and further resources. A novice does not have to read every supporting document before understanding why a first action matters.
Know what the guide does not confer
This is the release of guidance, not a new law, commercial security product or certification scheme. Reading it does not award a business a NIST badge. Nor does the connection to CSF 2.0 establish that an owner has met every legal or contractual requirement that could apply to their work.
That boundary becomes important when a larger client requests particular security evidence. The owner needs to understand the actual request, not answer it with a general statement that they follow a guide. A useful resource can help prepare the business while leaving the specific obligation to be assessed in its own context.
NIST describes the publication as a narrower revision of the earlier Small Business Information Security: The Fundamentals, focused on protecting digital systems from malicious attack. Our examination uses the release description and publication record; it does not claim an implementation test. Take the new resource into the next working week with one named dependency and one action to examine. The practical gain is a clearer decision, not a guarantee that the worry has disappeared.
Sources
- NIST — original guide announcement ↗ NIST — original guide announcement · Primary source
- NIST CSRC — original publication record ↗ NIST CSRC — original publication record · Primary source
Have additional information? Request a correction.